A Russian ransomware gang breaches the Energy Department and other federal agencies
Advertisement
Read this article for free:
or
Already have an account? Log in here »
To continue reading, please subscribe:
Digital Subscription
One year of digital access for only $205*
- Enjoy unlimited reading on winnipegfreepress.com
- Read the E-Edition, our digital replica newspaper
- Access News Break, our award-winning app
- Play interactive puzzles
*First annual payment billed as $205.00 + GST for one year. This annual subscription will automatically renew at $233.00 + GST every 52 weeks (10% off the regular annual price of $259.35). Offer available to new and qualified returning subscribers only. Cancel any time.
To continue reading, please subscribe:
Add Free Press access to your Brandon Sun subscription for only an additional
$1 for the first 4 weeks*
- Enjoy unlimited reading on winnipegfreepress.com
- Read the E-Edition, our digital replica newspaper
- Access News Break, our award-winning app
- Play interactive puzzles
*Your next Brandon Sun subscription payment will increase by $1.00 and you will be charged $17.95 plus GST for four weeks. After four weeks, your payment will increase to $24.95 plus GST every four weeks.
Read unlimited articles for free today:
or
Already have an account? Log in here »
Hey there, time traveller!
This article was published 15/06/2023 (1209 days ago), so information in it may no longer be current.
The Department of Energy and several other federal agencies were compromised in a Russian cyber-extortion gang’s global hack of a file-transfer program popular with corporations and governments, but the impact was not expected to be great, Homeland Security officials said Thursday.
But for others among what could be hundreds of victims from industry to higher education — including patrons of at least two state motor vehicle agencies — the hack was beginning to show some serious impacts.
Jen Easterly, director of the Cybersecurity and Infrastructure Security Agency, told reporters that unlike the meticulous, stealthy SolarWinds hacking campaign attributed to state-backed Russian intelligence agents that was months in the making, this campaign was short, relatively superficial and caught quickly.
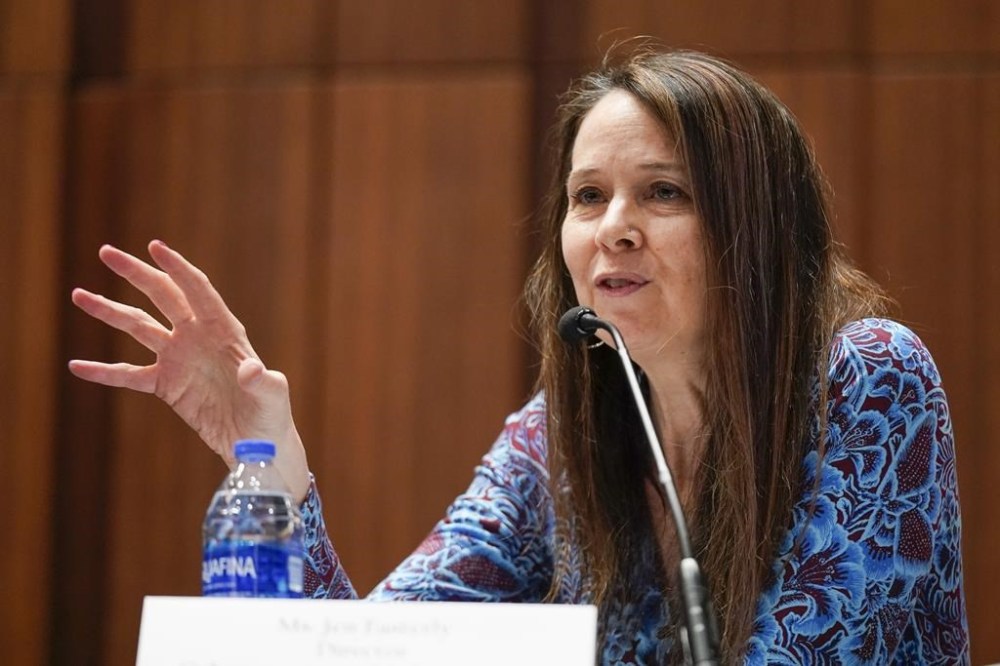
“Based on discussions we have had with industry partners … these intrusions are not being leveraged to gain broader access, to gain persistence into targeted systems, or to steal specific high value information— in sum, as we understand it, this attack is largely an opportunistic one,” Easterly said.
“Although we are very concerned about this campaign and working on it with urgency, this is not a campaign like SolarWinds that presents a systemic risk to our national security or our nation’s networks,” she added.
A senior CISA official said neither the U.S. military nor intelligence community was affected. Energy Department spokesperson Chad Smith said two agency entities were compromised but did not provide more detail.
Known victims to date include Louisiana’s Office of Motor Vehicles, Oregon’s Department of Transportation, the Nova Scotia provincial government, British Airways, the British Broadcasting Company and the U.K. drugstore chain Boots. The exploited program, MOVEit, is widely used by businesses to securely share files. Security experts say that can include sensitive financial and insurance data.
Louisiana officials said Thursday that people with a driver’s license or vehicle registration in the state likely had their personal information exposed. That included their name, address, Social Security number and birthdate. They encouraged Louisiana residents to freeze their credit to guard against identity theft.
The Oregon Department of Transportation confirmed Thursday that the attackers accessed personal information, some sensitive, for about 3.5 million people to whom the state issued identity cards or driver’s licenses.
The Cl0p ransomware syndicate behind the hack announced last week on its dark web site that its victims, who it suggested numbered in the hundreds, had until Wednesday to get in touch to negotiate a ransom or risk having sensitive stolen data dumped online.
The gang, among the world’s most prolific cybercrime syndicates, also claimed it would delete any data stolen from governments, cities and police departments.
The senior CISA official told reporters a “small number” of federal agencies were hit — declining to name them — and said “this is not a widespread campaign affecting a large number of federal agencies.” The official, speaking on condition of anonymity to discuss the breach, said no federal agencies had received extortion demands and no data from an affected federal agency had been leaked online by Cl0p.
U.S. officials “have no evidence to suggest coordination between Cl0p and the Russian government,” the official said.
The parent company of MOVIEit’s U.S. maker, Progress Software, alerted customers to the breach on May 31 and issued a patch. But cybersecurity researchers say scores if not hundreds of companies could by then have had sensitive data quietly exfiltrated.
“At this point, we are seeing industry estimates of several hundred of victims across the country,” the senior CISA official said. Federal officials encouraged victims to come forward, but they often don’t. The U.S. lacks a federal data breach law, and disclosure of hacks varies by state. Publicly traded corporations, health care providers and some critical infrastructure purveyors do have regulatory obligations.
The cybersecurity firm SecurityScorecard says it detected 2,500 vulnerable MOVEit servers across 790 organizations, including 200 government agencies. It said it was not able to break down those agencies by country.
The Office of the Comptroller of the Currency in the Treasury Department uses MOVEit, according to federal contracting data. Spokeswoman Stephanie Collins said the agency was aware of the hack and has been monitoring the situation closely. She said it was “conducting detailed forensic analysis of system activity and has not found any indications of a breach of sensitive information.” She would not say how the agency uses the file-transfer program.
The hackers were actively scanning for targets, penetrating them and stealing data at least as far back as March 29, said SecurityScorecard threat analyst Jared Smith.

This is far from the first time Cl0p has breached a file-transfer program to gain access to data it could then use to extort companies. Other instances include GoAnywhere servers in early 2023 and Accellion File Transfer Application devices in 2020 and 2021.
The Associated Press emailed Cl0p on Thursday asking what government agencies it had hacked. It did not receive a response, but the gang posted a new message on its dark web leak site saying: “We got a lot of emails about government data, we don’t have it we have completely deleted this information we are only interested in business.”
Cybersecurity experts say the Cl0p criminals are not to be trusted to keep their word. Allan Liska of the firm Recorded Future has said he is aware of at least three cases in which data stolen by ransomware crooks appeared on the dark web six to 10 months after victims paid ransoms.
—
AP reporters Sara Cline in Baton Rouge, Louisiana, Eugene Johnson in Seattle and Nomaan Merchant and Rebecca Santana in Washington contributed to this report.