2.5M Genworth policyholders and 769K retired California workers and beneficiaries affected by hack
Advertisement
Read this article for free:
or
Already have an account? Log in here »
To continue reading, please subscribe:

Digital Subscription
One year of digital access for only $205*
- Enjoy unlimited reading on winnipegfreepress.com
- Read the E-Edition, our digital replica newspaper
- Access News Break, our award-winning app
- Play interactive puzzles
*First annual payment billed as $205.00 + GST for one year. This annual subscription will automatically renew at $233.00 + GST every 52 weeks (10% off the regular annual price of $259.35). Offer available to new and qualified returning subscribers only. Cancel any time.
To continue reading, please subscribe:
Add Free Press access to your Brandon Sun subscription for only an additional
$1 for the first 4 weeks*
- Enjoy unlimited reading on winnipegfreepress.com
- Read the E-Edition, our digital replica newspaper
- Access News Break, our award-winning app
- Play interactive puzzles
*Your next Brandon Sun subscription payment will increase by $1.00 and you will be charged $17.95 plus GST for four weeks. After four weeks, your payment will increase to $24.95 plus GST every four weeks.
Read unlimited articles for free today:
or
Already have an account? Log in here »
Hey there, time traveller!
This article was published 22/06/2023 (1196 days ago), so information in it may no longer be current.
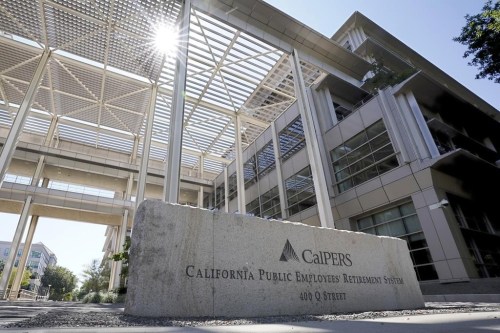
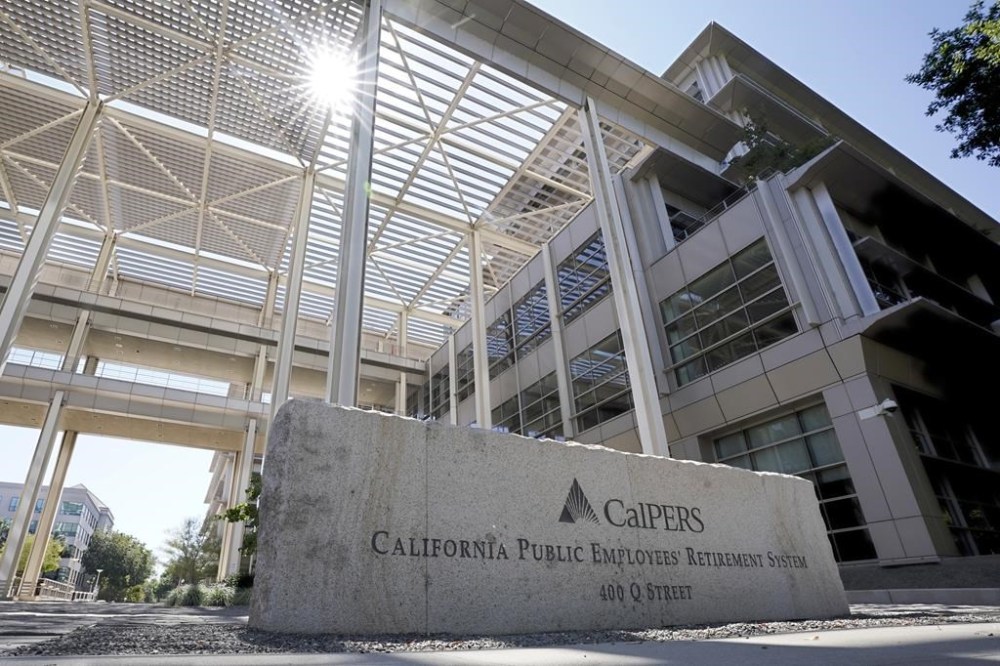
SACRAMENTO, Calif. (AP) — The country’s largest public pension fund says the personal information of about 769,000 retired California employees and other beneficiaries — including Social Security numbers — was among data stolen by Russian cybercriminals in the breach of a popular file-transfer application.
It blamed the breach on a third-party vendor that verifies deaths. The same vendor, PBI Research Services/Berwyn Group, also lost the personal data of at least 2.5 million Genworth Financial policyholders, including Social Security numbers, to the same criminal gang, according to the Fortune 500 insurer.
The California Public Employees Retirement system said they were offering affected members two years of free credit monitoring. Genworth said in a statement posted online it would offer credit monitoring and ID theft protection.
The breach of the MOVEit file-transfer program, discovered last month, is estimated by cybersecurity experts to have compromised hundreds of organizations globally. Confirmed victims include the U.S. Department of Energy and several other federal agencies, more than 9 million motorists in Oregon and Louisiana, Johns Hopkins University, Ernst & Young, the BBC and British Airways.
The criminal gang behind the hack, known as Cl0p, is extorting victims, threatening to dump their data online if they don’t pay up.
Genworth disclosed the hack Thursday of the MOVEit instance managed by PBI Research in a filing with the Securities and Exchange Commission.
Minnesota-based PBI Research did not immediately return a phone message seeking details on which of its other customers may have been affected. The company’s website lists the Nevada, New Jersey and Tennessee public pension funds as among customers of its mortality verification service.
“This external breach of information is inexcusable,” CalPERS CEO Marcie Frost said in a news release. “Our members deserve better. As soon as we learned about what happened, we took fast action to protect our members’ financial interests, as well as steps to ensure long-term protections.”
CalPERS had more than $442 billion in assets as of Dec. 31 and about 1.5 million members.
Security experts say such so-called supply-chain hacks expose an uncomfortable truth about the software organizations use: Network security is only as strong as the weakest digital link in the ecosystem.
The stolen data included names, birth dates and Social Security numbers — and might also include names of spouses or domestic partners and children, officials said. CalPERS planned to send letters Thursday to those affected by the breach.
CalPERS said PBI notified it of the breach on June 6, the same day cybersecurity firms began to issue reports on the breach of MOVEit, whose maker, Ipswitch, is owned by Progress Software.
PBI reported the breach to federal law enforcement, and CalPERS placed “additional safeguards” to protect the information of retirees who use the member benefits website and visit a regional office, officials said. The agency did not elaborate on those safeguards, citing security reasons.
___
This story has been corrected to reflect that Genworth disclosed the hack on Thursday, not June 16.
___
Bajak reported from Boston.
___
Sophie Austin is a corps member for the Associated Press/Report for America Statehouse News Initiative. Report for America is a nonprofit national service program that places journalists in local newsrooms to report on undercovered issues. Follow Austin on Twitter: @sophieadanna